Repository navigation
Payload contribution guide instructs contributors to clone upstream and push to origin (HTTP 403 failure) #63

Description

Website baseline: ac81655f4ac3aa1250023a3a9a5e3a93c00ac059 (website branch), checked locally on 2026-10-28.
Observed behavior
In src/app/contributing/page.tsx, the "Payload Submission Process" section outlines git instructions for contributing new payloads.
Step 1 is titled "1. Fork the upstream repository", but the code block instructs contributors to clone directly from upstream:
git clone https://github.com/owasp/owasp-hunting.git
cd owasp-hunting
Subsequently, Step 3 instructions tell contributors to push their branch to origin:
git push origin add-xss-payloadsBecause the clone command in Step 1 cloned the canonical OWASP/OWASP-Hunting.git repository, origin points to upstream where external contributors do not have push permissions. When a contributor attempts to run git push origin add-xss-payloads, the command fails with:
remote: Permission to OWASP/OWASP-Hunting.git denied to <username>
fatal: unable to access 'https://github.com/owasp/owasp-hunting.git/': The requested URL returned error: 403
Reproduction
- Navigate to
/contributing/. - Scroll to the "Payload Submission Process" section.
- Review the git workflow: Step 1 clones upstream, while Step 3 pushes to origin.
- Following these steps from a non-maintainer account results in a fatal HTTP 403 permission denied error.
Expected behavior
Update Step 1 to instruct contributors to clone their own fork:
git clone https://github.com/<your-username>/OWASP-Hunting.git
cd OWASP-Hunting
git remote add upstream https://github.com/OWASP/OWASP-Hunting.git
Or recommend using the GitHub CLI: gh repo fork OWASP/OWASP-Hunting --clone.
Note: This is distinct from #42, which addressed the directory cd target in the installation guide; this report concerns the push remote target and permissions failure in the payload contribution guide.
Marked screenshot
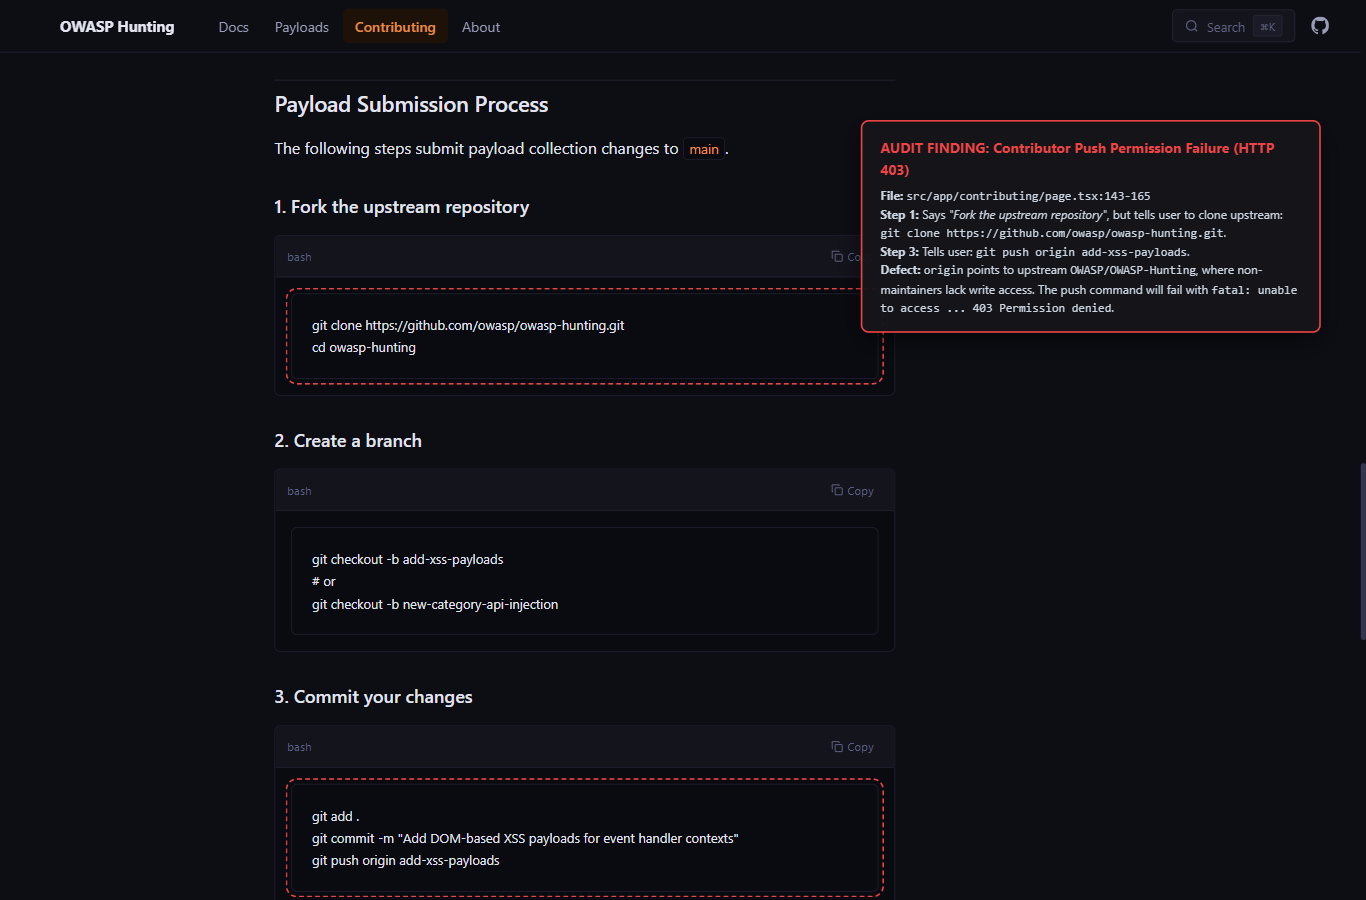
Red boxes, numbered callouts and AUDIT ANNOTATION panels were added temporarily in the browser to identify the observation/request. They are not implemented website features. Capture notes.
Source
Scope and disclosure
Issue report only; no PR or website code changes. AI assistance: Google Antigravity (Gemini); browser investigation via Playwright, evidence annotations and report drafting. Checks were executed locally; payload examples remained inert text; no target testing was performed.
Activity
Ashishchoudhary07 commentedon Oct 28, 2026
/take-pr
github-actions commentedon Oct 28, 2026
@Ashishchoudhary07 is now assigned to this issue.